The Debian Project has announced the release of Debian 13.8, the eighth maintenance update to its stable Debian 13 “Trixie” series, addressing multiple use-after-free vulnerabilities that could cause denial-of-service. It also fixes a Secure Boot bypass tracked as CVE-2026-97876.
An additional set of fixes concerns glibc. The update resolves numerous vulnerabilities, including buffer overflows, out-of-bounds writes, stack overflows, and concurrency issues. It also fixes problems that could cause applications to hang during UTF-32 conversion and improves CPU feature detection on Intel systems.
Intel microcode receives a new upstream release with security fixes for several processor vulnerabilities. Additionally, the Debian installer has been rebuilt with the Linux 6.12.117+deb13 ABI, in line with the updated kernel packages in this point release.
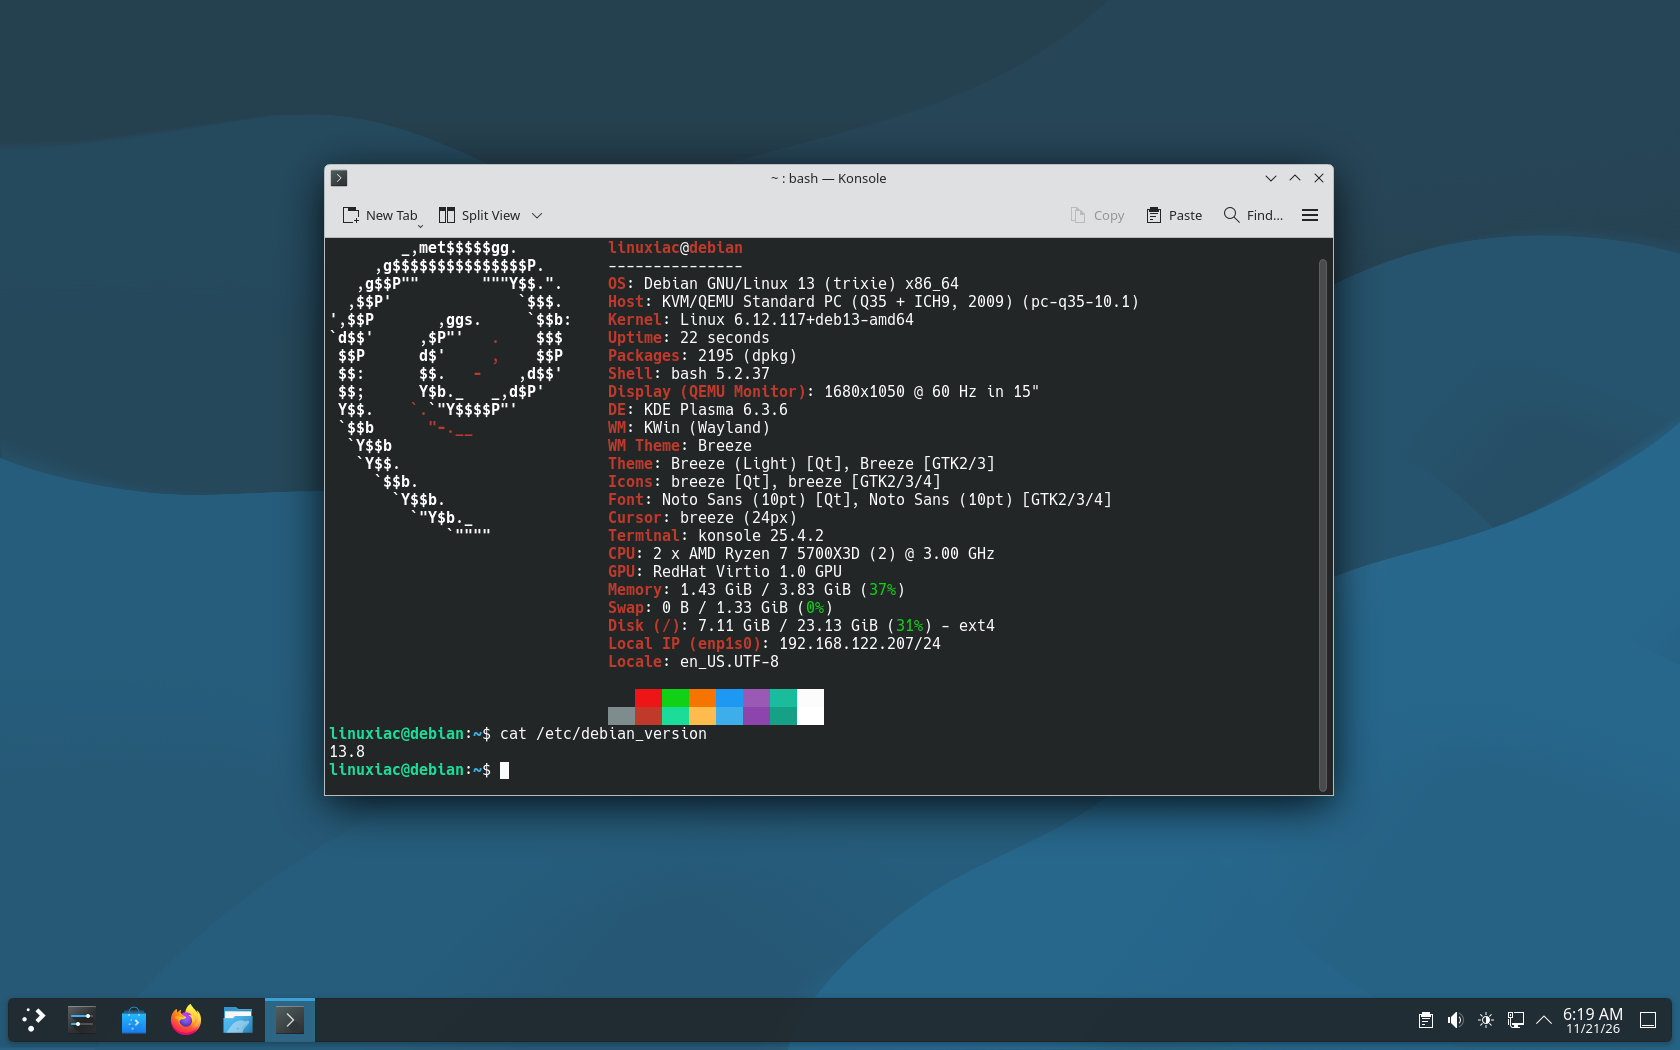
On the desktop side, KDE’s KWin window manager receives fixes for Wayland color management and crashes that could occur when disconnecting monitors.
The update also includes a new upstream stable MariaDB release that addresses several security issues, including code execution, authorization bypass, path traversal, and SQL injection vulnerabilities. Additional corrections resolve crashes, collation errors, and other database-related problems.
Other security improvements affect Rsync, which fixes an unauthenticated resource-exhaustion vulnerability, and Sudo, which addresses a security issue involving manipulation of the TZ environment variable. OpenSSL and ClamAV also receive updated upstream stable releases; the latter incorporates numerous security fixes.
For networking environments, both BIRD 2 and BIRD 3 receive corrections covering BGP timer calculations, authentication key handling, and FlowSpec validation. Other affected packages are ModSecurity, ProFTPD, SSSD, and various OpenStack components.
Beyond these package-specific corrections, Debian 13.8 incorporates previously published security updates for numerous applications and system components, including Firefox ESR, Chromium, LibreOffice, Nginx, PHP 8.4, Flatpak, OpenSSL, and the Linux kernel.
As with previous point releases, Debian 13.8 is not a new distribution version. Existing Debian 13 users can get the latest packages through the regular update mechanism: sudo apt update && sudo apt full-upgrade.
For more information, see the announcement.
If you are planning a fresh install, Debian 13.8 netinst ISO images are available for download here. They offer a base system ideal for servers or users who want to customize the installation to their needs, with support for six architectures: amd64, arm64, armhf, ppc64el, riscv64, and s390x.
For a ready-to-use experience, the new release also provides Live images with pre-installed desktop environments: GNOME, KDE, LXDE, Xfce, Cinnamon, and MATE. These are available only for the AMD64 architecture.